

Quick Summary
- Supply chain cyber threats are rising sharply in 2026.
- Organizations face new risks from geopolitical tensions.
- Effective strategies include increased transparency and automation.
- Supply chain attacks can disrupt critical infrastructure.
- Businesses are adopting more proactive security measures.
- Future risks involve AI-driven cyber threats.
Supply chain security in 2026 is more critical than ever as cyberattacks targeting suppliers and logistics networks surge. Recent incidents have exposed vulnerabilities in global supply chains, prompting urgent calls for stronger defenses.
With geopolitical tensions escalating and cybercriminals employing sophisticated tactics, organizations must understand evolving risks and adopt comprehensive strategies to protect their operations and data.
Supply Chain Security in 2026: Understanding the Core Risks
Supply chains are increasingly targeted by cybercriminals aiming to exploit weak links. Major breaches in 2025, like the attack on a leading logistics provider, underscored how interconnected vulnerabilities can ripple across industries.
Threat actors now use AI-powered malware, supply chain phishing campaigns, and third-party software exploits to infiltrate organizations. The CVE-2025-XXXX vulnerability in a widely-used logistics management system exemplifies these emerging risks.
Government agencies and industry groups have issued warnings about rising threats to critical infrastructure, emphasizing the need for heightened vigilance and layered security measures.
To learn more about recent supply chain cyberattack trends, see our detailed analysis in Supply Chain Cyberattack Risks in 2026.
Key Supply Chain Risks in 2026
- Targeted attacks on third-party vendors
- AI-driven malware and automation exploits
- Supply chain disruption from geopolitical conflicts
- Increased sophistication of phishing campaigns
- Vulnerabilities in legacy and IoT devices
"Supply chain security in 2026 demands proactive, layered defenses to counter increasingly sophisticated cyber threats."
Cybersecurity Expert
How Do Supply Chain Attacks Work in 2026?
Supply chain attacks typically involve infiltrating a less-secure partner or supplier to access the larger target. Hackers often exploit vulnerabilities in third-party software or hardware updates to gain entry.
Recent examples include compromised firmware updates and malicious code embedded in trusted vendor applications. These methods allow attackers to bypass traditional perimeter defenses.
Understanding how these attacks operate helps organizations implement targeted controls, such as code signing and continuous monitoring, to detect anomalies early.
For a technical breakdown, see our guide on Supply Chain Cybersecurity Risks in 2026.
Supply Chain Attack Techniques
- Compromised firmware updates
- Third-party software exploits
- Malicious vendor hardware
- Phishing targeting suppliers
- AI-powered malware deployment
"Attackers are leveraging AI and supply chain complexity to craft more convincing and harder-to-detect breaches."
Cybersecurity Analyst
Implications for Businesses and Critical Infrastructure
Supply chain breaches can cause widespread disruptions, impacting manufacturing, healthcare, and energy sectors. The fallout from a major attack could cost billions and compromise public safety.
Organizations must adopt zero trust principles, enhance supplier vetting, and increase visibility into their extended networks. Real-time monitoring and automated threat detection are critical.
Regulatory bodies are also stepping up, mandating stricter supply chain security standards. Non-compliance could lead to hefty fines and legal liabilities.
Learn more about compliance strategies in Zero Trust Security in 2026.
Why Supply Chain Security Matters in 2026
- Prevent widespread operational disruptions
- Protect sensitive data and IP
- Ensure regulatory compliance
- Safeguard critical infrastructure
- Reduce financial and reputational risks
"A resilient supply chain is vital for national security and economic stability in 2026."
Industry Security Expert
Comparing Traditional vs. Modern Supply Chain Security Approaches
Traditional security focused on perimeter defenses and endpoint protection. Today, this approach is insufficient against advanced supply chain threats.
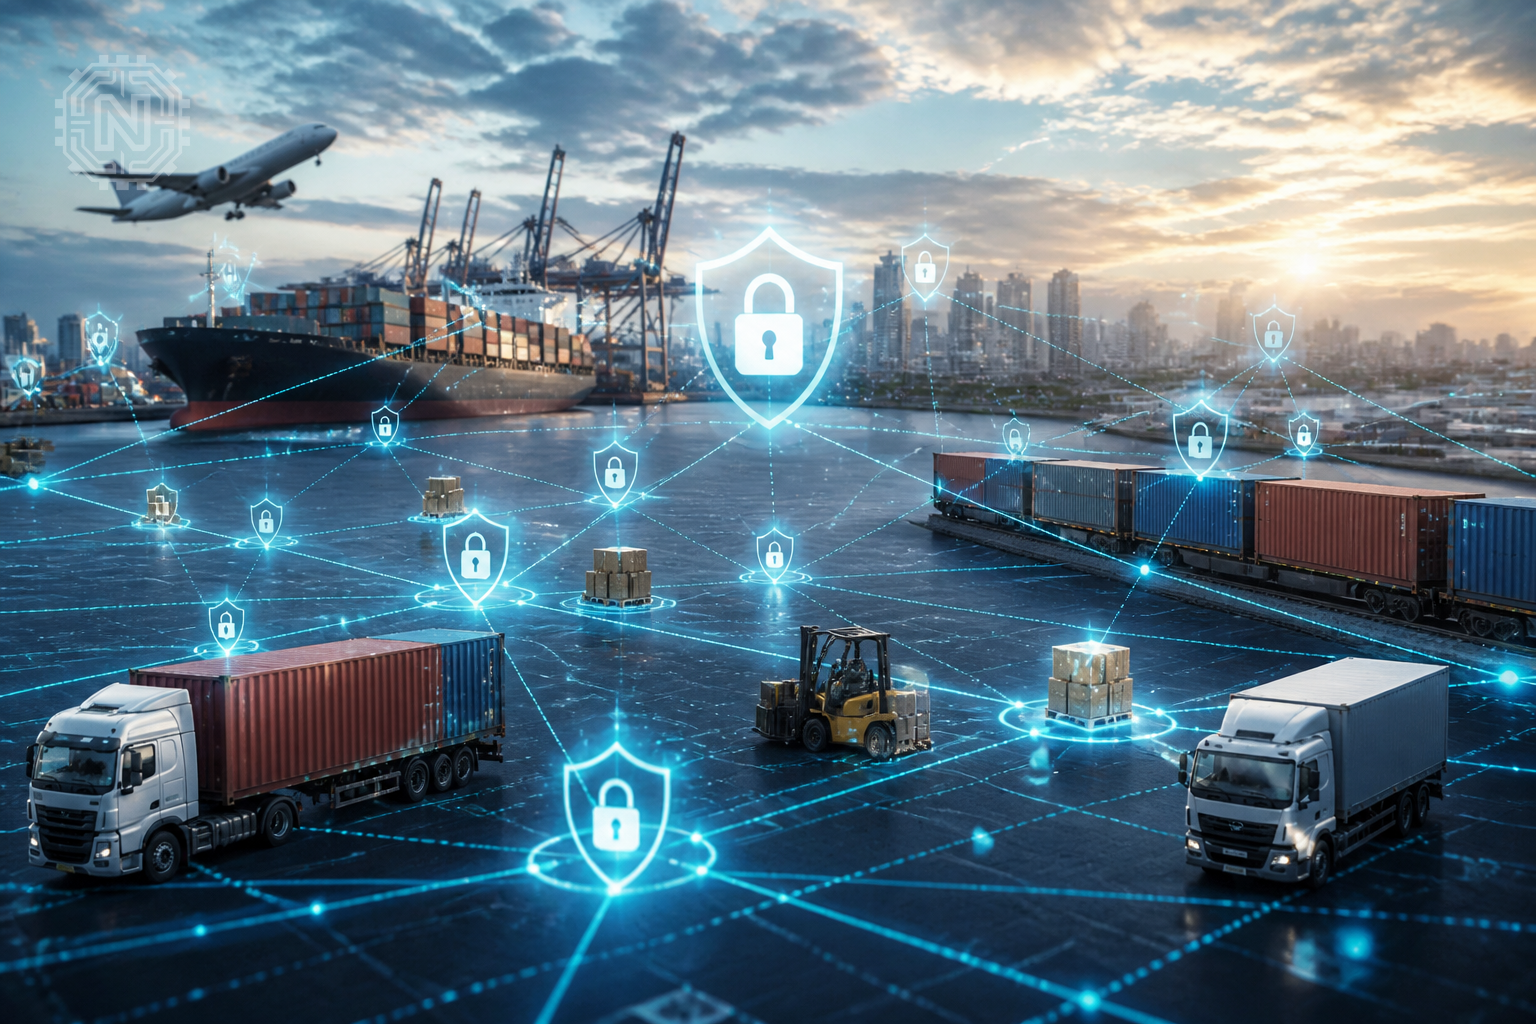
Modern strategies emphasize zero trust models, continuous risk assessment, and automation. These methods create a layered defense that adapts to evolving threats.
For a detailed comparison, see our analysis in Supply Chain Security in 2026: Critical Strategies for Protection.
Traditional vs. Modern Supply Chain Security
- Traditional: perimeter-focused, reactive
- Modern: zero trust, proactive
- Traditional: slower response times
- Modern: real-time threat detection
- Traditional: relies on legacy systems
"Adopting zero trust and automation is no longer optional; it's essential for supply chain resilience."
Cybersecurity Consultant
Future Outlook: What’s Next for Supply Chain Security?
Expect continued evolution in attack techniques, including AI-driven supply chain manipulations and deepfake vendor impersonations. Attackers will leverage increasingly complex supply networks.
Organizations will need to invest in AI-powered security tools, blockchain for transparency, and enhanced collaboration with suppliers and regulators.
Regulatory frameworks are likely to tighten, requiring more comprehensive reporting and compliance measures. Staying ahead of these changes is crucial.
Stay informed about emerging trends by following updates in Cybersecurity.
Future Supply Chain Security Trends
- AI-driven attack methods
- Blockchain for supply chain transparency
- Enhanced supplier security protocols
- Increased regulatory oversight
- Greater automation in threat detection
Editorial Sources
Conclusion
Supply chain security in 2026 is at a pivotal point. With cyber threats growing in sophistication and geopolitical tensions rising, organizations must adopt proactive, layered defenses. Staying ahead requires continuous monitoring, automation, and collaboration across the supply chain ecosystem.
Frequently Asked Questions
What are the biggest supply chain security threats in 2026?
Key threats include AI-powered malware, third-party exploits, and geopolitical disruptions targeting supply networks.
How can organizations protect their supply chains from cyberattacks?
Implement layered defenses like zero trust, continuous monitoring, supplier vetting, and automation to detect and prevent breaches.
Are supply chain attacks more sophisticated now?
Yes, attackers use AI, deepfakes, and complex malware to breach supply chains, making defenses more challenging.
What role does automation play in supply chain security?
Automation enables real-time threat detection, rapid response, and continuous risk assessment, reducing human error.
How will regulations affect supply chain cybersecurity?
Expect stricter standards, mandatory reporting, and increased oversight to ensure better security practices.
What future trends should organizations prepare for?
AI-driven attacks, blockchain transparency, and increased collaboration with suppliers will shape future security strategies.
Is zero trust effective for supply chain security?
Yes, zero trust provides a proactive, layered approach that minimizes attack surfaces and improves resilience.
How much does supply chain security cost?
Costs vary widely depending on size and complexity but investing in prevention is crucial to avoid costly breaches. For more on Cybersecurity, explore Newtechzy. You can also review our Privacy Policy and Cookie Policy, or learn more About us.
Related Topics
Ensure your supply chain is prepared for 2026. Explore our detailed strategies and get expert advice today to safeguard your operations.
Start Your Journey Today!


