

Quick Summary
- Zero Trust assumes no device or user is trustworthy by default.
- Recent breaches highlight the importance of Zero Trust in 2026.
- Implementation involves strict identity verification and micro-segmentation.
- Major organizations report improved security posture after adopting Zero Trust.
- Challenges include complex deployment and integration costs.
- Future trends point toward AI-driven Zero Trust solutions.
In 2026, Zero Trust Security remains the most talked-about cybersecurity approach, gaining widespread adoption across industries. It fundamentally shifts traditional perimeter defenses, requiring continuous verification of every user and device attempting to access resources.
With cyberattacks becoming more sophisticated, organizations can't rely solely on firewalls or VPNs. Zero Trust offers a proactive framework to prevent breaches by reducing attack surfaces and enforcing strict access controls.
Understanding Zero Trust Security in 2026
Zero Trust Security is a cybersecurity model that operates on the principle of 'never trust, always verify.' It assumes that threats can exist both outside and inside the network, making continuous authentication essential.
Developed in response to rising data breaches and insider threats, Zero Trust emphasizes least-privilege access, micro-segmentation, and real-time monitoring. Leading firms like Microsoft and Google have integrated Zero Trust into their security architectures, setting industry standards.
For a comprehensive overview, see Supply Chain Security in 2026 and Zero Trust Strategies in 2026.
Key Zero Trust Principles in 2026
- Continuous identity verification for all users and devices.
- Micro-segmentation to limit lateral movement.
- Least privilege access policies enforced dynamically.
- Real-time activity monitoring and anomaly detection.
- Integration with AI for automated threat response.
"Zero Trust is no longer optional; it's essential in defending against today's complex cyber threats."
Cybersecurity Expert
How Zero Trust Security Works in Practice Today
Implementing Zero Trust involves deploying multi-factor authentication (MFA), deploying micro-segmented networks, and applying strict access controls based on user identity and device health.
Organizations often use identity providers like Okta or Azure AD to manage authentication and access policies. Meanwhile, network segmentation tools isolate sensitive data and critical systems from general network traffic.
Real-time monitoring solutions, such as SIEMs and endpoint detection, help identify suspicious activity early. For example, a recent report noted that companies using Zero Trust saw a 60% reduction in lateral movement during breaches.
Learn more about implementing Zero Trust in our How-To guides or explore latest cybersecurity news for updates on deployment trends.
Pros and Cons of Zero Trust in 2026
- Enhanced security posture and breach containment.
- Reduces insider threat risks.
- Supports compliance with data protection standards.
- Deployment complexity and costs can be high.
- Requires cultural shift and staff training.
Official Adoption and Industry Reactions
Major tech firms like Google, Microsoft, and Cisco have publicly committed to Zero Trust frameworks, integrating them into their cloud and enterprise solutions.
The U.S. government has mandated Zero Trust architectures for federal agencies, reflecting its importance in national security. The NIST Special Publication 800-207 provides detailed guidelines.
Industry analysts note that Zero Trust is becoming a baseline requirement rather than an optional add-on, with the market for Zero Trust solutions expected to grow at a CAGR of over 20% through 2026.
For more insights, see our coverage of recent cybersecurity developments.
"Adopting Zero Trust is no longer a choice but a necessity for organizations aiming to stay resilient."
Cybersecurity Analyst
Practical Implications and Business Impact of Zero Trust
Implementing Zero Trust can significantly reduce the risk of data breaches, especially in sectors handling sensitive information like finance, healthcare, and government.
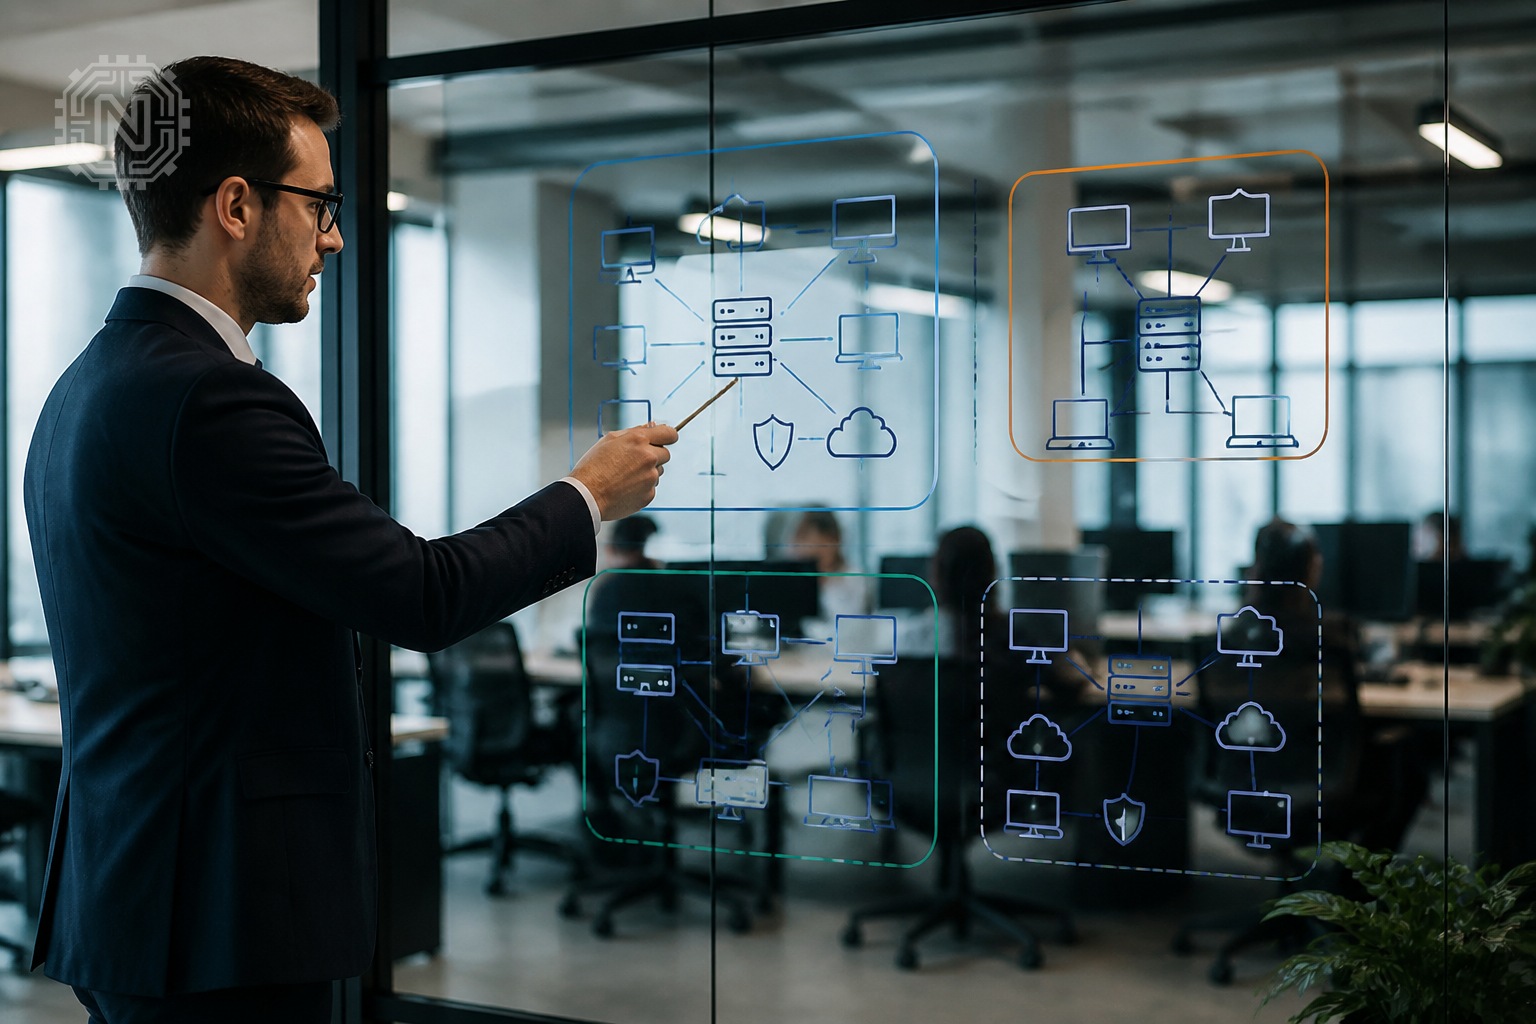
Organizations report improved incident response times and better compliance with regulations such as GDPR and HIPAA. However, the transition demands careful planning, staff training, and investment in security infrastructure.
Small and medium enterprises (SMEs) are increasingly adopting Zero Trust to level the playing field against cybercriminals, as attacks no longer target only large corporations.
To start your Zero Trust journey, consider assessing your current architecture and prioritizing high-value assets for initial segmentation.
Why Zero Trust Matters in 2026
- Prevents lateral movement during attacks.
- Reduces attack surface exposure.
- Supports compliance and audit readiness.
- Requires cultural change within organizations.
Future Outlook: Zero Trust and Emerging Technologies
Looking ahead, AI and machine learning will play pivotal roles in automating Zero Trust policies, enabling faster threat detection and response.
Edge computing and IoT devices pose new challenges for Zero Trust, demanding more granular and adaptive security measures.
Research indicates that by 2030, Zero Trust architectures will be standard across all sectors, driven by regulatory mandates and cyber threat evolution.
Stay updated with our latest articles on cybersecurity trends and innovations shaping the future.
Zero Trust Future Trends
- AI-driven automated policy enforcement.
- Enhanced security for IoT and edge devices.
- Integration with zero-day threat detection systems.
- Greater emphasis on user behavior analytics.
Editorial Sources
Conclusion
As cyber threats continue to evolve, Zero Trust Security remains the most effective approach for safeguarding critical assets. Organizations adopting this model are better positioned to prevent breaches, respond swiftly to incidents, and comply with emerging regulations. The shift is already underway, making Zero Trust an essential part of modern cybersecurity strategies.
Frequently Asked Questions
What is Zero Trust Security in simple terms?
Zero Trust Security is a cybersecurity approach that requires continuous verification of users and devices before granting access.
Why is Zero Trust important in 2026?
It reduces the risk of data breaches and insider threats, especially as cyberattacks become more sophisticated.
How does Zero Trust differ from traditional security?
Unlike traditional models, Zero Trust does not trust any device or user by default, enforcing strict access controls constantly.
Can small businesses adopt Zero Trust?
Yes, many SMEs are implementing Zero Trust to protect sensitive data and compete against larger organizations.
What are the main challenges of Zero Trust deployment?
Challenges include high initial costs, complex integration, and the need for staff training and organizational change.
What future technologies will enhance Zero Trust?
AI and machine learning will automate policy enforcement and threat detection, making Zero Trust more adaptive.
Is Zero Trust mandatory for government agencies?
Yes, many governments, including the US, require federal agencies to adopt Zero Trust architectures.
How long does it take to implement Zero Trust?
Implementation varies but can take several months to over a year depending on organization size and complexity. For more on Cybersecurity, explore Newtechzy. You can also review our Privacy Policy and Cookie Policy, or learn more About us.
Related Topics
Explore how your organization can implement Zero Trust today. Contact our security experts for tailored advice and solutions.
Start Your Journey Today!


