

Quick Summary
- Zero Trust assumes no implicit trust within networks, requiring continuous verification.
- Recent breaches highlight the importance of Zero Trust in preventing lateral movement.
- Implementing Zero Trust involves strict identity verification, micro-segmentation, and real-time monitoring.
- Organizations adopting Zero Trust see reduced breach impact and improved compliance.
- The approach aligns with evolving regulations and increasing remote work demands.
- Future developments include AI-driven Zero Trust models and automation.
In 2026, Zero Trust Security remains the most effective framework to combat sophisticated cyberattacks. It shifts the traditional perimeter-based security model, requiring continuous verification of users, devices, and applications.
As cyber threats grow more complex and remote work becomes the norm, organizations must adopt Zero Trust principles to safeguard sensitive data and maintain operational resilience.
Understanding Zero Trust Security in 2026: Background and Core Principles
Zero Trust Security is a cybersecurity approach that assumes no device or user is inherently trustworthy, even inside the network. Instead, it enforces strict identity verification and continuous monitoring to minimize risk.
Originally introduced by Forrester Research in 2010, Zero Trust gained widespread adoption after high-profile breaches exposed vulnerabilities in perimeter defenses. Today, it’s a fundamental part of modern cybersecurity architectures.
Key principles include least privilege access, micro-segmentation, and real-time analytics. These ensure that even if an attacker breaches one part of the network, lateral movement is prevented.
For more on foundational concepts, see our Cybersecurity category and latest tech news.
Zero Trust in a Nutshell
- Assumes no implicit trust inside or outside the network.
- Requires continuous authentication and authorization.
- Utilizes micro-segmentation to isolate workloads.
- Relies on real-time monitoring and analytics.
- Supports remote and hybrid work environments effectively.
What Happened in 2026: Recent Developments in Zero Trust Security
Throughout 2026, Zero Trust has become the standard for enterprise cybersecurity. Major vendors like Microsoft, Palo Alto Networks, and Cisco have released new Zero Trust solutions tailored for hybrid and remote workforces.
The U.S. government issued updated cybersecurity mandates emphasizing Zero Trust frameworks for federal agencies, reinforcing its importance across sectors.
High-profile breaches, such as the recent ransomware attack on a multinational corporation, underscored the need for Zero Trust to contain threats and limit damage.
For a detailed overview of recent security incidents, visit CISA’s official site.
"Zero Trust continues to evolve, integrating AI and automation to stay ahead of attackers."
Cybersecurity Analyst
How Zero Trust Works: Deeper Mechanics and Implementation Strategies
Implementing Zero Trust involves deploying identity and access management (IAM) systems that enforce strict authentication, such as multi-factor authentication (MFA) and biometrics.
Micro-segmentation divides networks into smaller zones, limiting the spread of malware and lateral movement.
Real-time analytics monitor activity for anomalies, enabling rapid response to threats.
Organizations also leverage Zero Trust Network Access (ZTNA) solutions to secure remote connections without exposing the entire network.
For practical guidance, see our how-to guides on Zero Trust deployment.
Zero Trust Implementation Challenges
- Requires significant initial investment and planning.
- Complexity in managing micro-segmented environments.
- Potential user friction if not implemented smoothly.
- Ongoing monitoring demands resources and expertise.
Official Reactions and Industry Perspectives on Zero Trust in 2026
Major cybersecurity firms have doubled down on Zero Trust strategies, emphasizing its role in future-proofing defenses. Their latest reports highlight the importance of integrating Zero Trust with existing security measures.
Government agencies worldwide are adopting Zero Trust frameworks, with the U.S. Department of Homeland Security endorsing comprehensive adoption by 2028.
Experts warn that successful Zero Trust implementation depends on organizational culture and ongoing staff training.
See NIST’s guidelines for official standards and best practices.
"Zero Trust is no longer optional; it’s a necessity for resilient cybersecurity."
Chief Security Officer
Implications and Practical Takeaways for Organizations in 2026
Adopting Zero Trust principles reduces the attack surface and limits damage from breaches. It’s especially critical for organizations with remote or hybrid workforces.
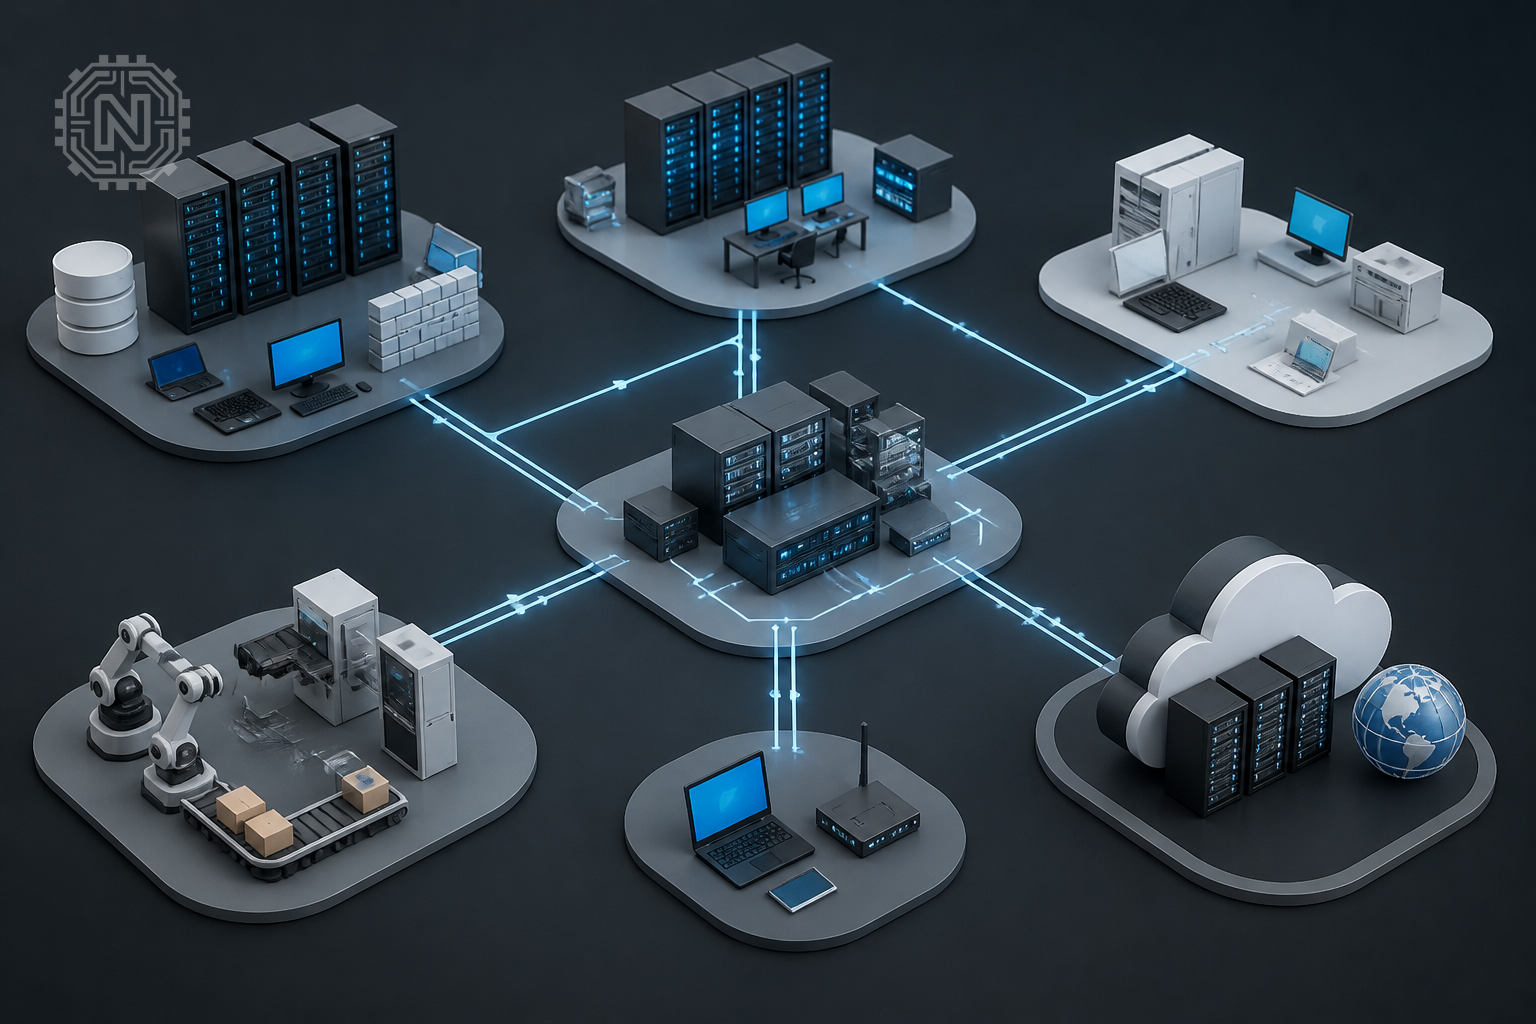
Practically, this means implementing MFA, network micro-segmentation, and continuous monitoring as standard practices.
Organizations should also invest in staff training and incident response planning aligned with Zero Trust frameworks.
For tailored advice, consult supply chain security strategies and other best practices.
Why Zero Trust Matters in 2026
- Prevents lateral movement during breaches.
- Supports compliance with increasing regulations.
- Enables secure remote and hybrid work models.
- Reduces overall risk exposure.
Future Outlook: Zero Trust and Evolving Cyber Threats
Looking ahead, Zero Trust will incorporate AI-driven automation and machine learning to detect threats faster and more accurately.
Emerging technologies like Zero Trust Edge aim to extend protections to IoT devices and edge computing environments.
Organizations that embrace these advancements will stay resilient against increasingly sophisticated cyberattacks.
For ongoing updates, follow our cybersecurity coverage.
Editorial Sources
Conclusion
Zero Trust Security remains a cornerstone of cybersecurity in 2026, with organizations adopting more sophisticated, automated, and integrated approaches to protect against evolving threats. Its principles of continuous verification and micro-segmentation are vital for resilience in an increasingly digital and remote world.
Frequently Asked Questions
What is Zero Trust Security and why is it important in 2026?
Zero Trust Security assumes no trust inside or outside the network, requiring continuous verification to protect against advanced cyber threats.
How do organizations implement Zero Trust in 2026?
Implementation involves multi-factor authentication, micro-segmentation, real-time monitoring, and Zero Trust Network Access solutions.
What are common challenges when adopting Zero Trust?
Challenges include high initial costs, managing micro-segments, user friction, and ongoing resource requirements.
Can Zero Trust prevent all cyberattacks?
While it significantly reduces risk, no security model is foolproof; continuous adaptation is essential.
How does AI influence Zero Trust security?
AI enhances threat detection, automates responses, and improves real-time analytics within Zero Trust frameworks.
Is Zero Trust suitable for small businesses?
Yes, with scalable solutions, Zero Trust principles can protect small businesses from sophisticated attacks.
What standards govern Zero Trust implementations?
NIST provides comprehensive guidelines and standards for Zero Trust deployment and best practices.
What is the future of Zero Trust security?
Future trends include AI-driven automation, edge protections, and integration with IoT security. For more on Cybersecurity, explore Newtechzy. You can also review our Privacy Policy and Cookie Policy, or learn more About us.
Related Topics
Stay ahead of cyber threats by adopting Zero Trust strategies today. Explore our detailed guides and expert insights to strengthen your defenses.
Start Your Journey Today!


