

Quick Summary
- Supply chain attacks increased by 35% in 2026, impacting global organizations.
- Recent breaches exploited software supply chain vulnerabilities.
- Effective defense requires comprehensive vendor security assessments.
- Automation and AI are key tools in threat detection and response.
- Organizations face complex challenges in managing third-party risks.
Supply chain cybersecurity in 2026 faces unprecedented challenges as hackers exploit vulnerabilities across interconnected vendor networks. Recent high-profile breaches have underscored the importance of securing every link in the supply chain to prevent cascading failures.
With attacks becoming more sophisticated, organizations must adapt their security strategies, integrating advanced monitoring, supplier vetting, and real-time threat intelligence to stay ahead of evolving risks.
Understanding supply chain cybersecurity risks in 2026
Supply chain cybersecurity involves protecting the entire network of suppliers, vendors, and third-party partners from cyber threats. In 2026, the landscape has shifted dramatically, with attackers targeting less secure links to gain access to larger enterprise systems.
Recent incidents, such as the breach of a major software provider in early 2026, revealed how vulnerabilities in third-party code can cascade into widespread compromises. These attacks often exploit outdated software, poor vendor security practices, or supply chain management gaps.
According to SANS Institute, nearly 60% of organizations experienced a supply chain attack in 2026, emphasizing the need for rigorous third-party risk management. Learn more about supply chain security strategies to mitigate these risks.
Key Supply Chain Security Facts
- Over 35% increase in supply chain attacks in 2026
- Most breaches exploit third-party software vulnerabilities
- Vendor security gaps remain the leading threat source
- Automation helps detect threats faster
- Organizations adopting zero-trust models see fewer breaches
"Supply chain cybersecurity is no longer optional; it’s a critical component of organizational resilience."
Cybersecurity Analyst
How do supply chain cyberattacks work and why are they so effective?
Supply chain attacks often start with compromising a trusted vendor or supplier, then leveraging their access to infiltrate larger targets. Attackers use techniques like malicious updates, software tampering, or credential theft.
For example, in 2026, a compromised software update from a popular provider led to malware infections across hundreds of organizations. These attacks are effective because they exploit the trust relationships that organizations rely on.
Understanding the mechanics helps organizations implement better defenses, such as verifying software authenticity, monitoring vendor activity, and segmenting networks. For more on latest attack vectors, see our detailed analysis.
"Attackers are increasingly exploiting supply chain trust to bypass traditional defenses."
Security Researcher
What are the most common vulnerabilities exploited in supply chain attacks?
Vulnerabilities include outdated software, weak vendor security practices, and poor supply chain visibility. Attackers often exploit unpatched systems or misconfigured third-party access points.
In 2026, CVE-2026-XXXX, a critical flaw in a widely used development platform, was exploited in multiple breaches. Organizations must prioritize patch management and vulnerability scanning.
Implementing comprehensive third-party assessments and continuous monitoring can mitigate these risks. For in-depth vulnerability management strategies, visit Zero Trust Security in 2026.
Vulnerabilities in Supply Chain Attacks
- Outdated software and unpatched systems
- Poor vendor security practices
- Weak access controls in third-party systems
- Lack of supply chain visibility
- Insufficient vulnerability management
How are organizations responding to supply chain cybersecurity threats?
Many firms are adopting zero-trust architectures, requiring continuous verification of all users and devices. Others are increasing investments in supply chain risk management tools.
Leading companies are conducting regular vendor security audits, integrating AI-based threat detection, and fostering closer collaboration with suppliers. These measures help reduce attack surfaces.
According to CSO Online, 75% of organizations plan to increase supply chain security budgets in 2026. For practical steps, see our guide on supply chain defense strategies."Proactive supply chain security measures are essential to prevent costly breaches."
Cybersecurity Executive
What are the best practices for securing the supply chain in 2026?
Effective strategies include comprehensive vendor assessments, implementing zero-trust models, and deploying automation for real-time threat detection.
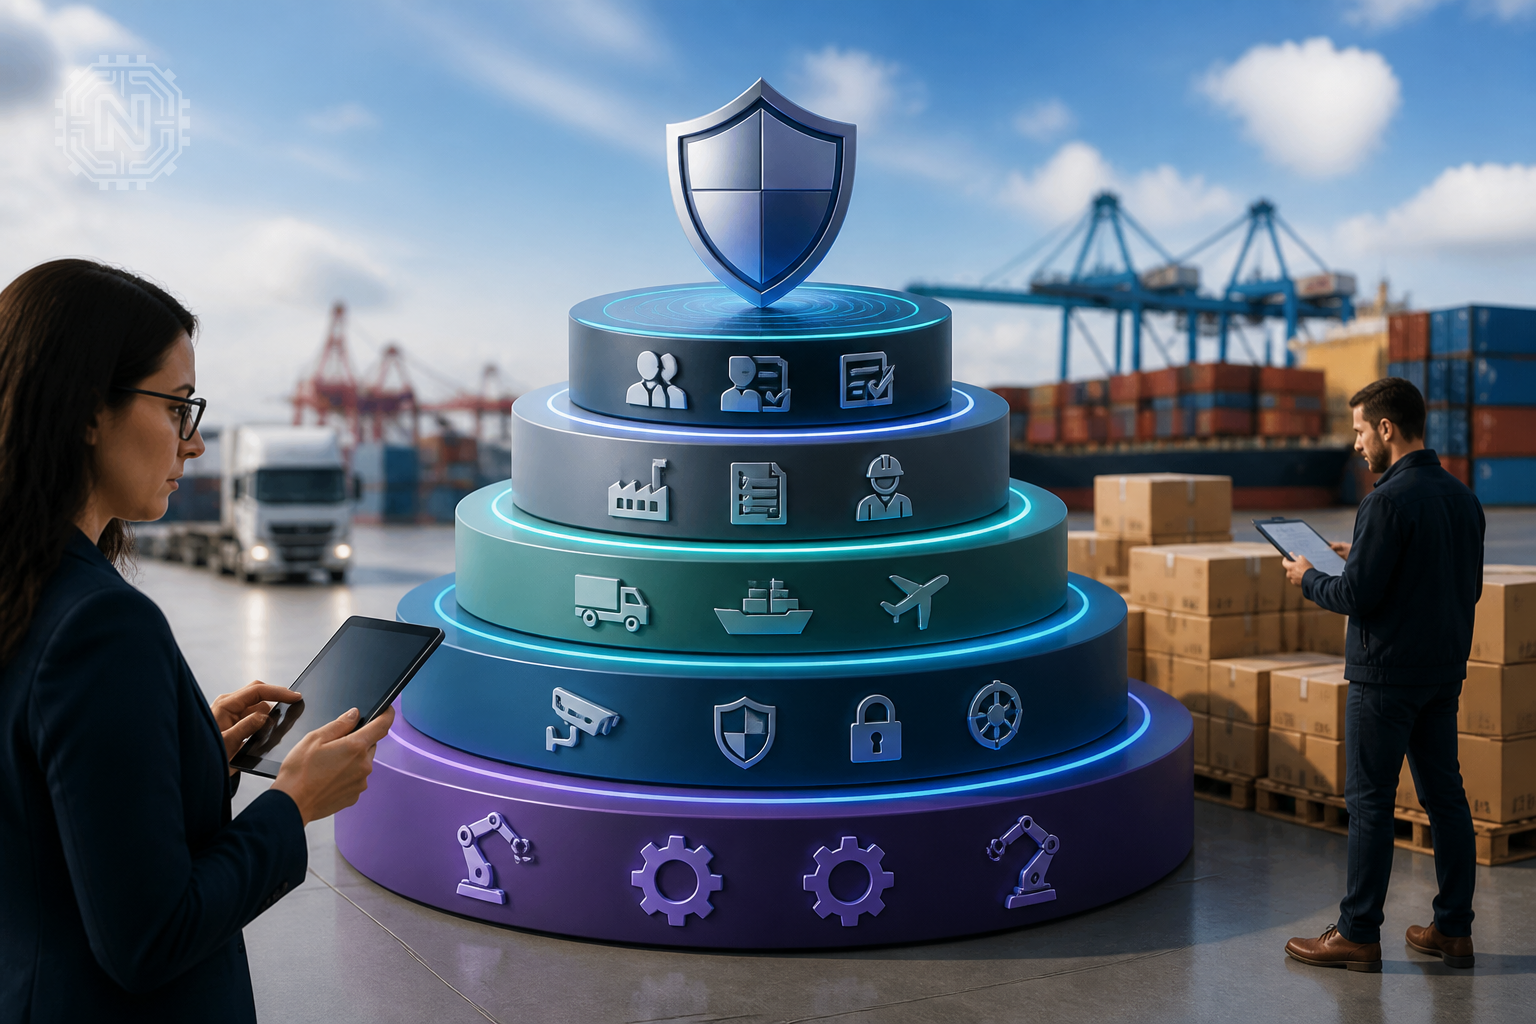
Organizations should also foster transparency and collaboration with suppliers, enforce strict access controls, and maintain updated vulnerability management programs.
Learn more about best practices for supply chain security to stay resilient against evolving threats.Why Supply Chain Security Matters in 2026
- Supply chain breaches can cause widespread operational disruption
- Attackers target less secure vendors to access larger networks
- Regulatory pressures demand higher security standards
- Falling victim leads to financial and reputational damage
Looking ahead: the future of supply chain cybersecurity
As technology advances, so do attack methods. Future threats may involve AI-driven malware and more sophisticated supply chain manipulations.
Organizations that adopt integrated security frameworks, leverage automation, and prioritize vendor security will be better positioned to defend against future attacks.
For ongoing updates, follow our coverage on cybersecurity trends and ensure your supply chain remains resilient.Editorial Sources
- Supply Chain Security in 2026: Protecting Critical Infrastructure
- Cybersecurity Risks in Supply Chains — NIST
- Latest Supply Chain Attacks and Defense Strategies — CSO Online
- Supply Chain Security Best Practices — Gartner
- Vulnerabilities and Threats in Supply Chain — ENISA
- Supply Chain Cyberattack Reports — Verizon Data Breach Investigations Report
- Understanding Supply Chain Attacks — MITRE ATT&CK Framework
Conclusion
Supply chain cybersecurity in 2026 is more critical than ever. Organizations must adopt proactive, layered defenses and collaborate closely with suppliers to reduce vulnerabilities and prevent costly breaches. Staying ahead of evolving threats requires continuous vigilance and innovation.
Frequently Asked Questions
What is supply chain cybersecurity?
Supply chain cybersecurity involves protecting interconnected vendor networks from cyber threats to prevent breaches.
Why are supply chain attacks increasing in 2026?
Attackers exploit vendor vulnerabilities and software supply chains, making breaches more frequent and impactful.
How can organizations defend against supply chain cyberattacks?
Implement zero-trust models, conduct vendor assessments, and deploy real-time threat detection tools.
What vulnerabilities are most exploited in supply chain breaches?
Outdated software, weak access controls, and poor supply chain visibility are common targets.
Are supply chain cyberattacks costly?
Yes, breaches can cause operational disruptions, financial loss, and reputational damage.
What role does automation play in supply chain security?
Automation speeds up threat detection, vulnerability management, and incident response.
How important is vendor security assessment?
Critical—assessing third-party security helps identify and mitigate potential risks early.
What is the future outlook for supply chain cybersecurity?
Increased use of AI, automation, and stricter standards will shape the future of supply chain security. For more on Cybersecurity, explore Newtechzy. You can also review our Privacy Policy and Cookie Policy, or learn more About us.
Related Topics
Protect your organization today by reviewing your supply chain security strategies. Explore our expert guides and get in touch for tailored advice.
Start Your Journey Today!


