

Quick Summary
- AI companies are collecting more user data than ever in 2026.
- New privacy regulations are being implemented worldwide.
- Many users remain unaware of how their data is used.
- Major breaches highlight ongoing security vulnerabilities.
- Tech giants are investing in privacy-enhancing AI.
- Users should review app permissions and privacy settings.
AI privacy in 2026 is under intense scrutiny as organizations gather massive amounts of personal data. With AI models becoming more integrated into daily life, understanding how your information is protected or exploited is crucial.
This article explores the latest developments in AI privacy, what regulations are shaping the landscape, and practical steps you can take to safeguard your data today.
AI Privacy in 2026: The evolving landscape and core issues
As AI systems become more sophisticated, the amount of personal data collected by companies has skyrocketed. From social media to smart devices, AI-driven platforms now process billions of data points daily.
Despite promises of privacy, many users remain in the dark about how their information is used, stored, and shared. Recent breaches and scandals have highlighted vulnerabilities, prompting calls for stricter regulations and transparency.
Major players like Google, Meta, and Microsoft are investing heavily in privacy-preserving technologies, but critics argue these efforts are often insufficient or merely superficial. The core challenge remains: balancing innovation with user rights.
For a deeper understanding of the regulatory environment, see AI chatbot privacy concerns 2026 and AI chip market 2026.
Key Facts About AI Privacy in 2026
- Data collection rates have increased by over 50% since 2024.
- Over 60 countries have enacted new privacy laws in the past two years.
- Major data breaches exposed millions of users' personal info in 2026.
- Leading AI firms are deploying privacy-focused algorithms.
- Users are increasingly aware but often lack practical control.
"AI privacy is now a fundamental concern, requiring both regulatory oversight and user vigilance."
Cybersecurity Expert
What happened / core details of AI privacy issues in 2026
Early in 2026, a series of high-profile data breaches at major tech firms revealed vulnerabilities in AI systems handling sensitive user data. These incidents exposed millions of personal records, sparking widespread concern.
Simultaneously, regulatory bodies like the European Data Protection Board and the U.S. FTC have proposed stricter guidelines for AI data handling, aiming to enforce transparency and accountability.
For example, recent updates to the GDPR include specific provisions on AI data processing, with fines for non-compliance reaching billions of dollars.
Companies now face the challenge of balancing AI innovation with compliance and user trust, leading to a surge in privacy-focused AI development.
Did You Know?
- Over 70% of AI companies now use encryption for user data.
- Many firms have adopted privacy-by-design principles since 2025.
"Regulatory pressure is pushing AI developers to prioritize privacy, but the pace of technological change often outstrips legal frameworks."
Tech Policy Analyst
How does AI handle user data and what are the mechanics?
AI systems process user data through complex algorithms that analyze patterns, preferences, and behaviors. Data is often collected via apps, IoT devices, and online platforms.
Data flows into centralized servers or cloud platforms where AI models train and generate insights. Techniques like federated learning are gaining popularity as privacy-preserving methods.
Federated learning enables AI to learn from data locally on devices, reducing the need for raw data transmission. This approach is promoted by companies like Google and Apple to enhance privacy.
To learn more about these techniques, see AI chip advancements 2026.
Federated Learning: Pros and Cons
- Pros: Keeps raw data on device, reduces breach risk.
- Cons: More complex to implement, may reduce model accuracy.
Official statements and reactions to AI privacy concerns
Leading companies have publicly committed to enhancing user privacy. Meta’s CEO announced new privacy safeguards in early 2026, emphasizing transparency and user control.
Regulators like the FTC and the European Commission have increased scrutiny, with new fines and regulations targeting non-compliance.
However, critics argue that corporate commitments often fall short, citing ongoing data collection practices and opaque AI training methods.
For official company policies, visit Meta’s privacy policy.
"While companies pledge to improve, actual privacy protections lag behind AI development pace."
Privacy Advocate
Practical implications and how users can protect their data
Users should regularly review app permissions, disable unnecessary data sharing, and use privacy tools like VPNs and encrypted messaging apps.
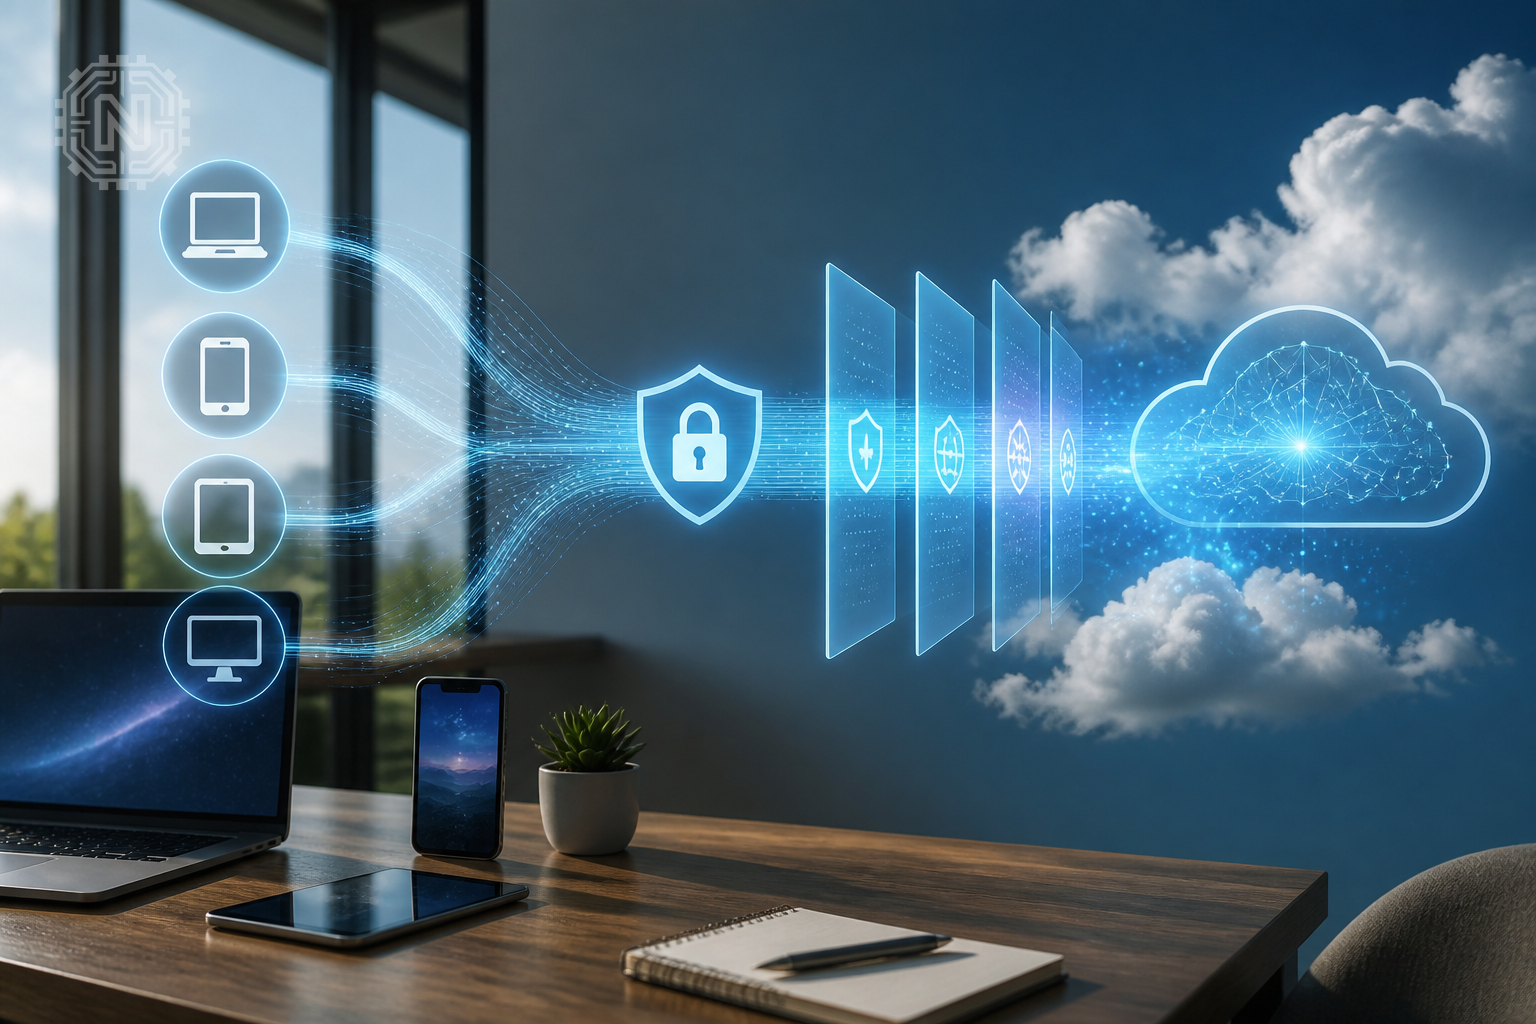
Many platforms now offer privacy dashboards—use these to monitor and control what data is collected and how it’s used.
Educating yourself about AI data collection practices is vital. Look for transparency reports and privacy notices from service providers.
To learn more about protecting your digital footprint, see privacy policy and how-to guides.
Why AI Privacy Matters in 2026
- Protects personal identity from misuse and theft.
- Builds trust in AI-driven services.
- Ensures compliance with legal standards.
Why AI privacy matters and future outlook
As AI becomes more embedded in everyday life, safeguarding privacy isn’t optional. Future legislation, like the upcoming US AI Act, aims to enforce stricter data protections.
Technological innovations such as differential privacy and secure multiparty computation will likely become standard tools for privacy preservation.
Experts predict that by 2030, AI privacy will be a core feature, not an afterthought, with user rights prioritized alongside technological progress.
Stay informed on developments through AI chip market 2026 and AI-powered search 2026.
Editorial Sources
Conclusion
AI privacy is a dynamic and critical issue in 2026, with ongoing regulatory changes and technological innovations shaping how personal data is protected. Users must stay vigilant by understanding their rights and leveraging available tools to secure their information amid evolving threats.
Frequently Asked Questions
What is AI privacy and why is it important in 2026?
AI privacy involves protecting personal data processed by AI systems, which is crucial as data collection increases and regulations tighten.
How do AI systems collect user data?
AI systems gather data through apps, IoT devices, and online services, analyzing patterns to improve functionalities and user experiences.
Are there new laws affecting AI privacy in 2026?
Yes, countries like the EU and US have introduced stricter privacy laws requiring transparency and accountability in AI data handling.
What can users do to protect their data in AI-powered services?
Review app permissions, enable privacy settings, use encryption tools, and stay informed about data collection practices.
What is federated learning and how does it improve privacy?
Federated learning trains AI models locally on devices, reducing raw data transmission and enhancing user privacy.
Are companies genuinely committed to AI privacy?
Many are investing in privacy tech, but critics argue actual protections often lag behind corporate promises.
What future trends will shape AI privacy?
Emerging technologies like differential privacy and stricter legislation will likely make AI data handling more secure.
How does GDPR impact AI privacy in 2026?
GDPR enforces strict data processing rules, demanding transparency and giving users control over their personal information. For more on Tech News, explore Newtechzy. You can also review our Privacy Policy and Cookie Policy, or learn more About us.
Related Topics
Explore our in-depth guides on protecting your digital privacy and stay ahead of AI privacy developments. Get in touch for personalized advice.
Start Your Journey Today!


